Work & Software Systems
Production services in Go, open-source diagnostic utilities, memory-safe cryptographic tools in Rust, and self-published commercial products.
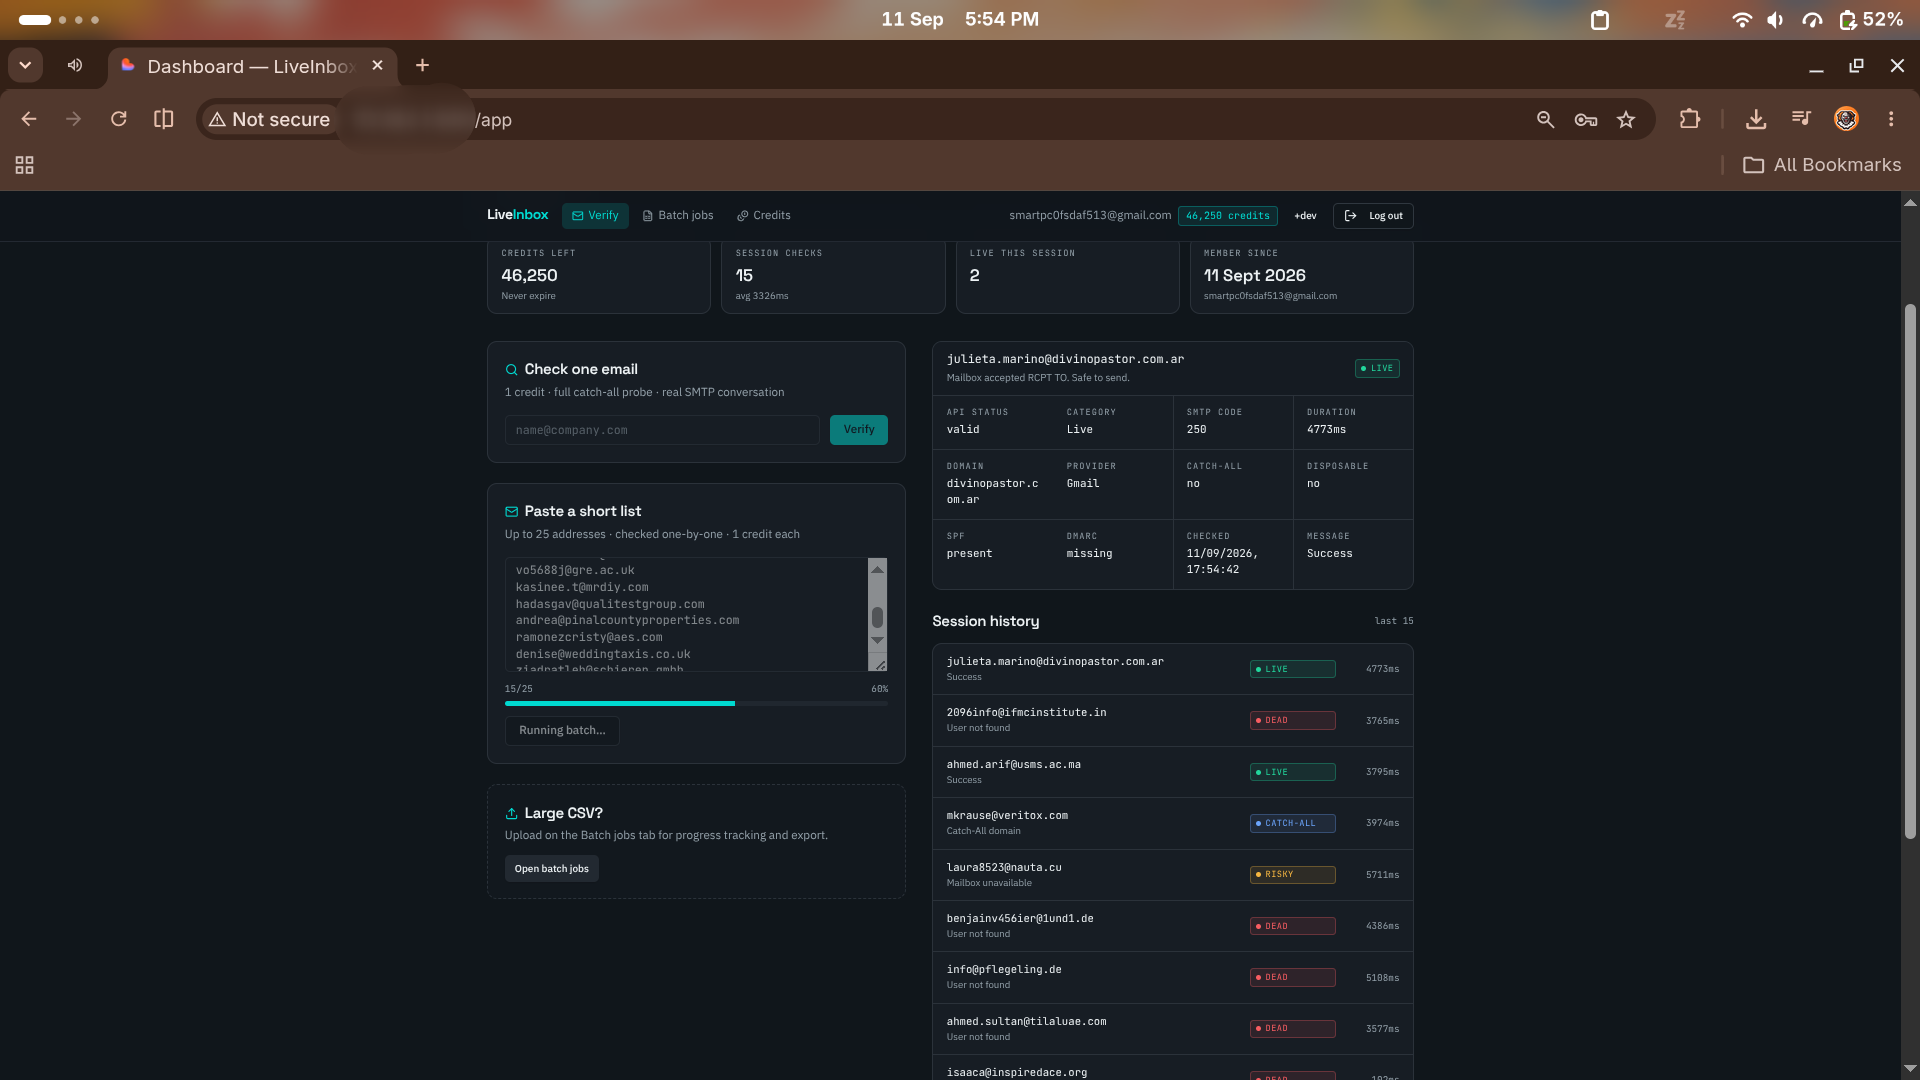
LiveInbox
Go / chi / RedisProprietary SaaSA specialized email deliverability system built in Go to test recipient mailboxes via non-intrusive SMTP RCPT TO negotiation without delivering messages.
Implementation Architecture
- Custom Go verification core using raw network sockets to initiate multi-stage SMTP handshakes (EHLO -> MAIL FROM -> RCPT TO) and evaluate SMTP reply codes (250 OK, 550 User Not Found).
- DNS resolver engine querying domain MX priority records and caching results to prevent redundant lookup overhead.
- Custom token-bucket rate limiting engine to throttle external server handshakes and eliminate IP ban risks.
- Clean REST API layer built with the chi router in Go, backed by PostgreSQL for persistent verification history and Redis for queueing and session caching.
- Full containerization via Docker Compose (database, cache, and API) with DigitalOcean and Nginx deployment.
dbradar
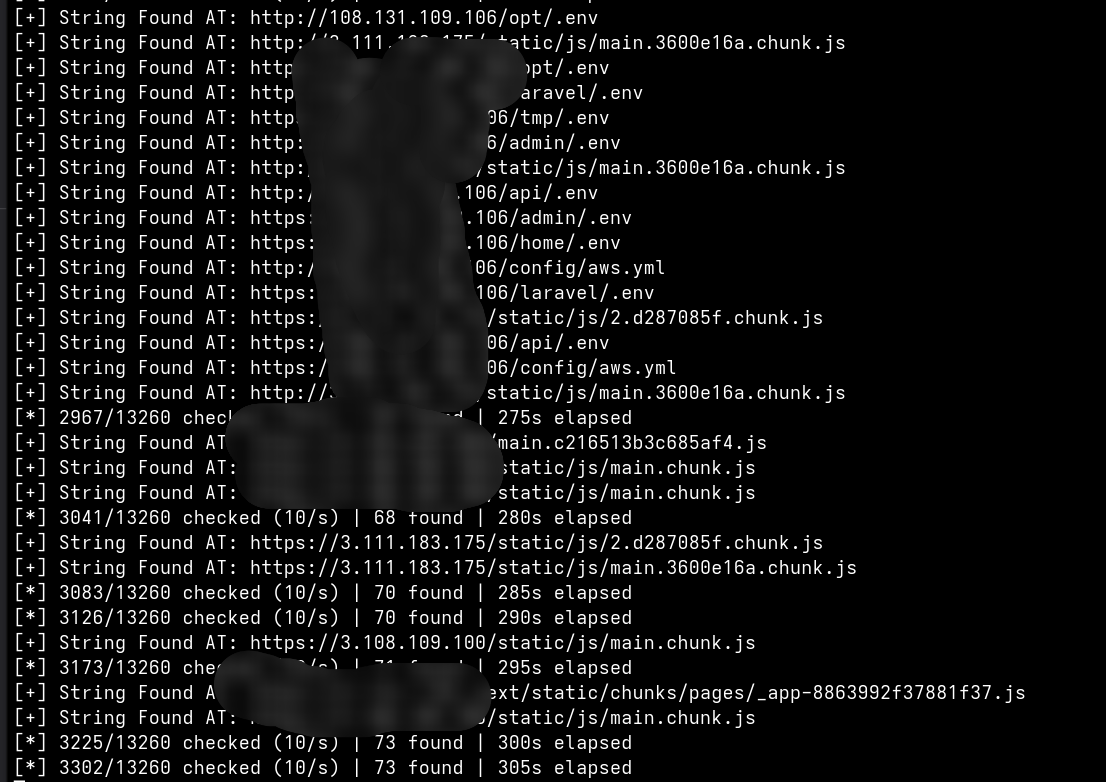
GoOpen Source CLIA fast, zero-dependency diagnostic utility designed for benchmarking connection pools, query latencies, and server telemetry directly from the terminal.
Implementation Architecture
- Lightweight Go binary designed to benchmark database responsiveness and connection pool exhaustion without third-party agent overhead.
- Concurrent target scanner capable of pacing checks at 10+ req/s with detailed timing logs and real-time elapsed statistics.
- Pure Go implementation with zero external runtime libraries for immediate execution on minimal Linux server distributions.
rustpass
RustOpen Source CLIA memory-safe command-line suite for generating, benchmarking, and verifying cryptographic password hashes with zero heap leaks.
Implementation Architecture
- Engineered in Rust to harness strict borrow-checking and ownership guarantees, ensuring cryptographic secrets are wiped from memory buffers.
- Implements modern password hashing algorithms including Argon2id, bcrypt, and scrypt with configurable work factors.
- Designed for systems administrators and automated deployment pipelines needing deterministic credential hashing without runtime bloat.
password_checker
PythonOpen Source ToolAutomated credential audit tool evaluating password complexity against Shannon entropy models, dictionary substitutions, and breach datasets.
Implementation Architecture
- Computes statistical Shannon entropy alongside pattern matching against top 100k breached passwords.
- Designed for authorized defensive assessments, active directory credential auditing, and automated compliance gates.
- Lightweight scripting easily hooked into CI/CD pipelines and local pre-commit hooks.
Security Recon & Custom Test Payloads
Bash / Python / NmapAuthorized EngagementsA curated suite of automated reconnaissance scripts, network diagnostic harnesses, and input validation test suites for permissioned audits.
Implementation Architecture
- Automated service discovery pipelines wrapping Nmap and socket sweeps to identify misconfigured ports and outdated protocol implementations.
- Documented client reporting workflow ensuring testing remains strictly scoped and adheres to established rules of engagement.
- Custom authentication stress test harnesses utilizing Hydra with strict rate limits to prevent target service degradation.
Bunkbar
Digital Product / GumroadCommercial PublicationA commercial digital fitness guide independently researched, authored, typeset, and launched online with end-to-end payment handling and customer fulfillment.
Implementation Architecture
- Full product lifecycle execution: market validation, structured content creation, PDF typesetting, and pricing tiers.
- Configured automated distribution infrastructure via Gumroad with payment gateway integration, tax calculation, and instant delivery.
- Operates active customer support, feedback loops, and iteration cycles.
All network reconnaissance tools, test payloads, and penetration scripts are authored strictly for defensive validation, lab experiments, and authorized testing under signed scopes.